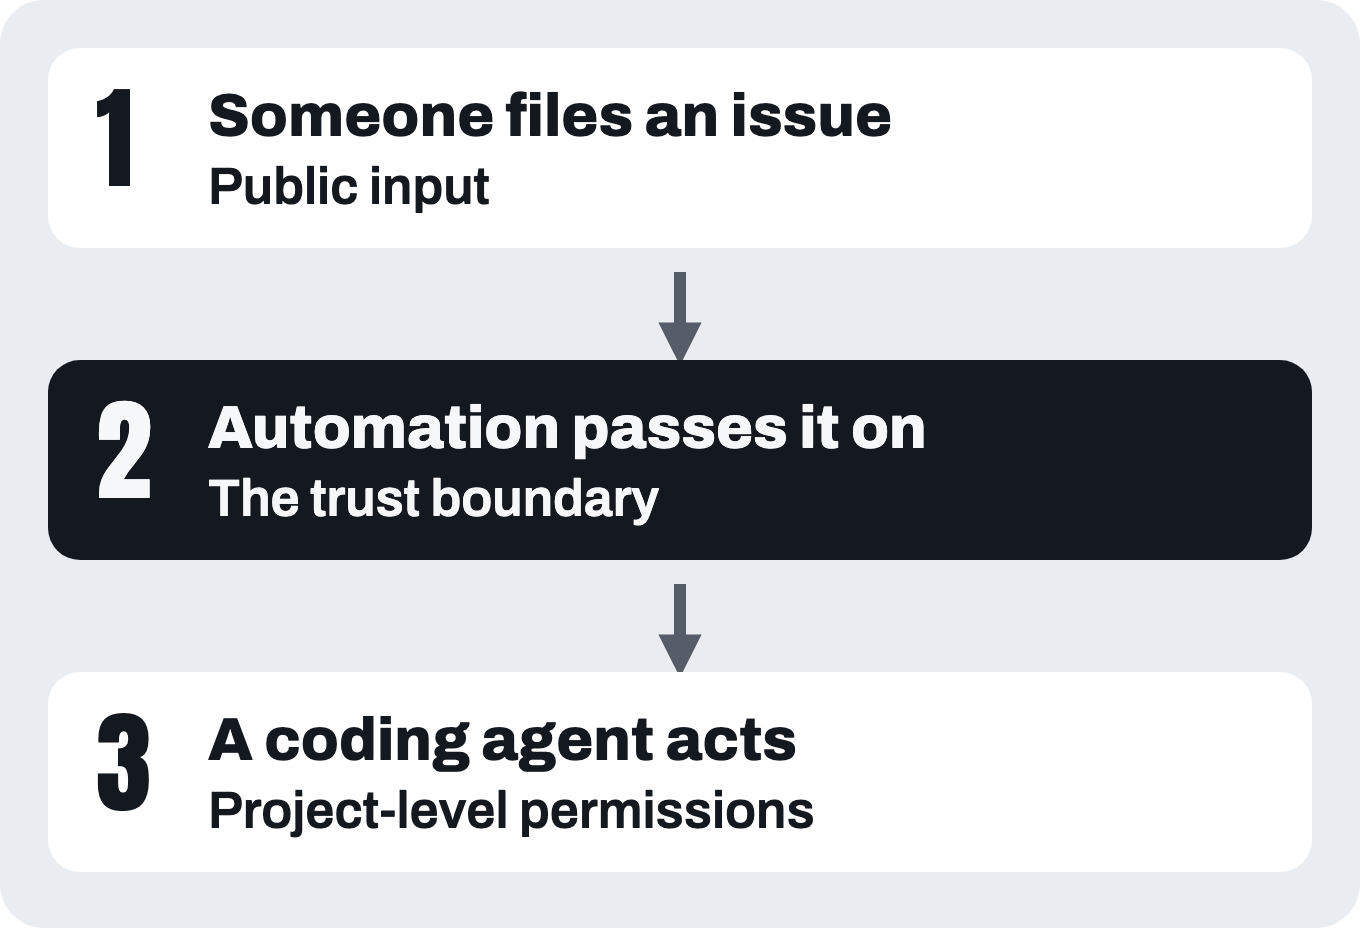
People file GitHub issues to describe bugs and request changes. Some projects have automated workflows that hand those reports to coding agents. Security researcher Elad Meged showed how that pairing could let a person without project access influence software that ran with project privileges.


Novee Security's disclosure describes tests involving coding-agent workflows from Anthropic, Google and OpenAI. The reported paths differ. Some led to code running on the worker machine that handles automation. Others exposed credentials or touched files later agents would read. Each case depended on the permissions and configuration the workflow had been given.
Text can cross a permission boundary
The security boundary runs between what a stranger can submit and what the automation can do after reading it. An agent may need to inspect a report to understand a bug. That task alone does not require exposing every credential the workflow can use or every file it can change.
The disclosure describes specific demonstrations. The broader lesson comes from the mismatch in privileges: the issue is public, but the process deciding how to act on it may have access that the issue author never had.